Proactive Network Monitoring & Enterprise Network Engineering
Secure, high-performance network design, proactive telemetry monitoring, and structured cabling for businesses requiring high-availability connectivity.
Proactive Network Monitoring, Structured Cabling, & Enterprise Security in Southern California
What is enterprise network engineering and proactive network monitoring?
Enterprise network engineering covers the layout, installation, and configuration of your firewalls, switches, wireless access points, and structured cabling. Proactive network monitoring runs 24/7 telemetry checks on bandwidth, latency, and packet loss so our engineers spot failing switch ports or traffic bottlenecks before they knock your Southern California office offline.
Why is certified Cat6 and fiber structured cabling critical for business connectivity?
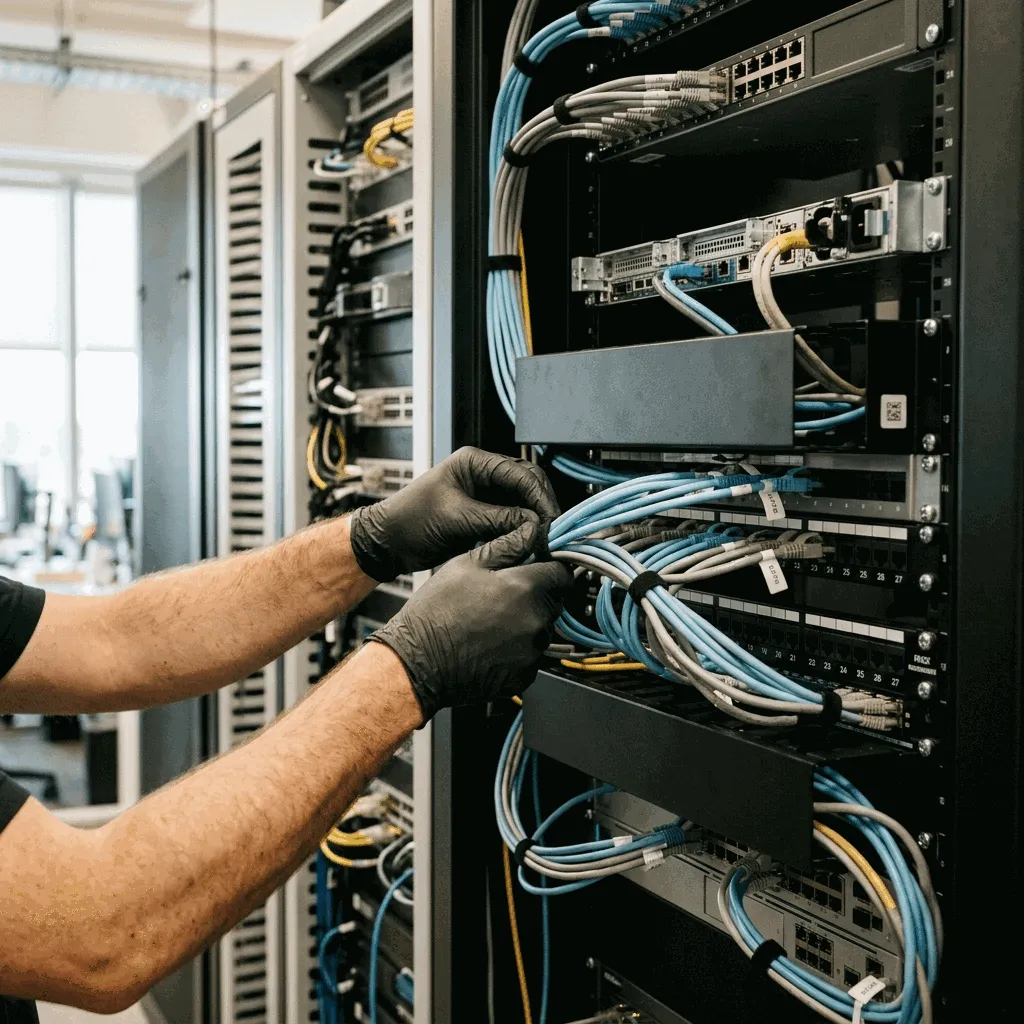
Bad physical wiring causes random disconnects that software fixes can never solve. Certified Cat6 and fiber-optic runs prevent electrical interference, stop packet collisions, and carry clean multi-gigabit traffic between your patch panels, VoIP desk phones, Wi-Fi 6 access points, and local servers.
As a Southern California MSP, Genesis builds and maintains commercial networks from the wiring closet out. We install encrypted site-to-site VPN tunnels, certified Cat6/fiber-optic cabling backbones, and warehouse or office Wi-Fi 6 layouts tuned for reliable throughput and clean VoIP calls.
Our Anaheim engineering team configures managed firewalls with active Intrusion Detection and Prevention Systems (IDS/IPS) and strict VLAN segmentation to keep payment terminals, medical records, and shop-floor machinery separated from guest and general office traffic.
Network engineering & monitoring work we handle
- 24/7 network monitoring, packet inspection, and switch port telemetry
- SonicWall NSA and TZ firewall staging (burn-in tested at 4055 E. La Palma Ave.)
- SCADA and industrial VLAN isolation for utilities, water districts, and plants
- Ruggedized warehouse Wi-Fi 6/6E and RF planning for steel racking aisles
- Encrypted site-to-site VPN tunnels and zero-trust remote access
- Structured voice and data cabling (Cat6, Cat6A, and fiber optic backbones)
Enterprise Network Infrastructure & Cabling Standards
Architectural comparison of physical cabling, wireless, and security perimeter standards deployed by Genesis network engineers across Southern California facilities.
| Features | Pricing/Tiers | Best For | Limitations |
|---|---|---|---|
Cat6 & Cat6A Structured Copper Cabling 1 Gbps to 10 Gbps (up to 100m runs), certified Fluke DTX/DSX diagnostic testing, TIA/EIA-568-C compliance, and plenum-rated (CMP) jackets. | $125 – $225 / dropIncludes patch panel termination, testing, and labeled faceplatesRequest a Quote → | Workstation wall drops, PoE IP security cameras, access control systems, VoIP desk phones, and high-density local patch bays. | Strict 100-meter channel distance limit; susceptible to severe electromagnetic interference (EMI) near heavy factory machinery. |
Fiber Optic Backbones (OM3/OM4 & Single-Mode) 10 Gbps to 100 Gbps high-speed interconnects, multi-kilometer reach, fusion splicing, complete immunity to EMI/RFI, and OTDR trace reports. | MDF-to-IDF campus links, inter-building warehouse risers, and low-latency storage area network (SAN) switch uplinks. | Higher hardware termination costs; requires fiber transceivers (SFP+/QSFP) on connected switches and specialized field termination tools. | |
High-Density Enterprise Wi-Fi 6 / 6E Up to 9.6 Gbps aggregate wireless throughput, WPA3 Enterprise 802.1X security, 6 GHz band spectrum, automated RF channel tuning, and guest isolation. | High-density commercial office spaces, conference centers, medical clinics, and zero-dead-spot commercial warehouse facilities. | Physical signal attenuation through reinforced concrete, metal industrial shelving, or foil insulation requiring dense AP placement. | |
Next-Gen UTM Firewall Gateways Multi-gigabit deep packet inspection, active Intrusion Prevention (IPS), gateway anti-malware, VLAN segmentation, and redundant SD-WAN failover. | Perimeter corporate defense, site-to-site VPN encryption between offices, remote workforce IPSec gateways, and PCI/HIPAA compliance boundary enforcement. | Requires active security definition subscriptions; deep SSL inspection requires trusted internal root certificate installation on endpoints. |
Pricing note: Published pricing applies to qualifying managed computers under the applicable agreement. Servers, network infrastructure, projects, onboarding, Microsoft licensing variations, after-hours support, and specialized compliance requirements may be quoted separately.
What counts as a computer: A computer refers to a managed Windows or Mac desktop or laptop workstation. Dedicated physical/virtual servers, network firewalls, specialized cloud tenants, and multi-site project deployments are quoted separately.